A dramatic leadership rupture has struck Automattic, the parent company of WordPress. The board has voted to...
WordPress
Sometimes a critical vulnerability doesn’t hide within a single flaw, but rather in the precise sequence of...

Last week, security researchers disclosed a remote code execution flaw in WordPress, the well-known content management system....
A single anonymous HTTP request can lead to code execution on a WordPress site, even if the...
After months of mounting tension within the WordPress community—marked by lawsuits and accusations of authoritarian control—the Linux...
The Eventin plugin, widely used for event management on WordPress websites, was found to be vulnerable to...
The OttoKit plugin for WordPress—installed on over 100,000 websites—has come under widespread attack exploiting two vulnerabilities, one...
One of the most prevalent attack vectors targeting WordPress involves disguising malicious code as a harmless plugin....
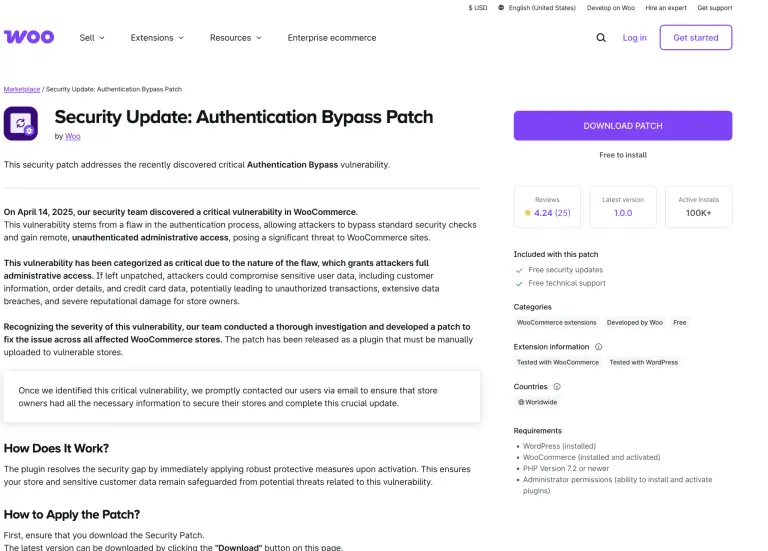
Specialists at Patchstack have uncovered a large-scale phishing campaign targeting users of the WooCommerce platform. Threat actors...
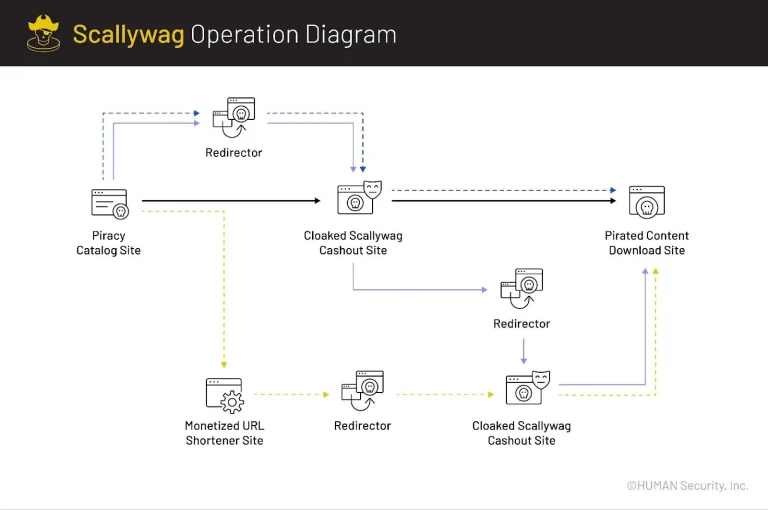
The fraudulent Scallywag scheme, built upon specially crafted WordPress plugins, had long been generating billions of ad...
Hackers have begun exploiting a critical vulnerability in the widely used WordPress plugin OttoKit (formerly known as...
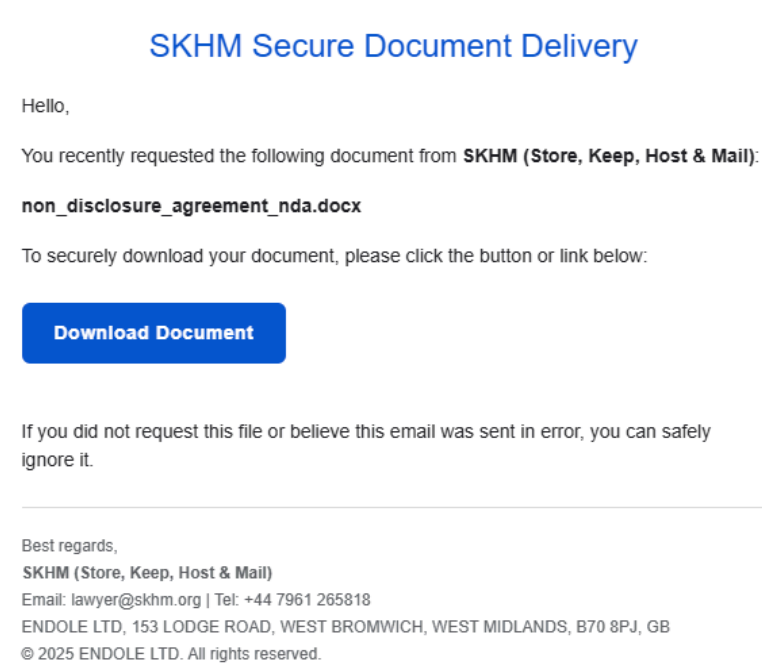
The Gootloader malware campaign has once again drawn attention — this time, the attackers have adopted a...
Since 2016, the DollyWay malware campaign has compromised more than 20,000 WordPress websites worldwide, redirecting unsuspecting users...