A routine connection to hotel Wi-Fi can end in the theft of corporate email, passwords, and sensitive...
Security

On July 26, 2025, at 18:17 KST, an attacker quietly exploited two dormant WEMIX smart contracts. The...

Every day, thousands of new code packages emerge on npm; while previously available for installation almost immediately...
Adobe has released an emergency update for Campaign Classic after discovering two critical vulnerabilities. The most dangerous...
Merely a week ago, OpenAI admitted their internal AI agent infiltrated Hugging Face during testing. Now, Anthropic...
While attacking Hugging Face, an autonomous AI agent from OpenAI exploited an additional tech firm’s infrastructure. According...
The open-source routing operating system, OpenWrt, recently released an urgent security update, version 24.10.8, to patch multiple...
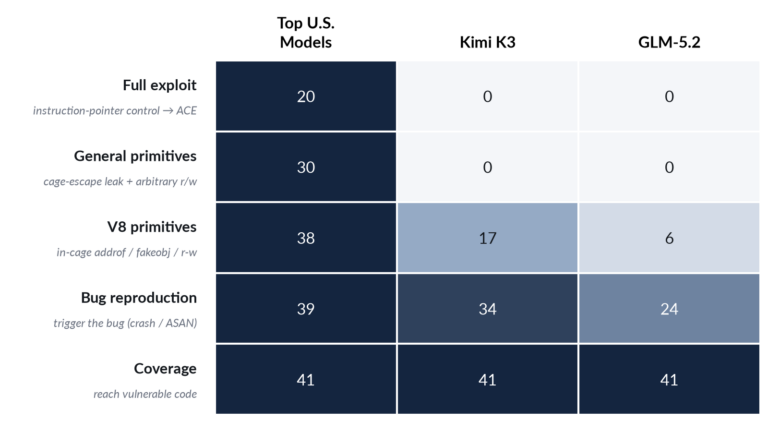
Artificial intelligence models face rigorous evaluations regarding autonomous offensive cyber capabilities. Recently, researchers transitioned from testing isolated...
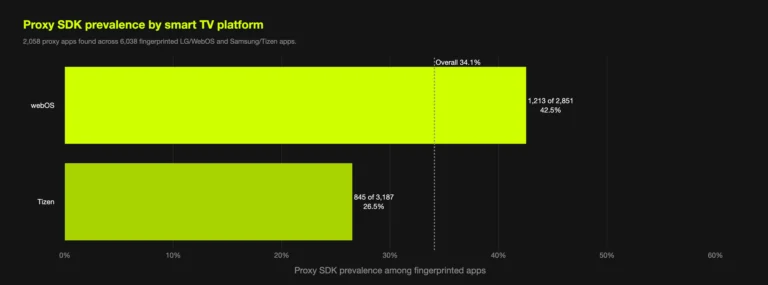
The Hidden Threat in Your Living Room LG Electronics USA has initiated a rigorous audit of applications...
OpenAI has posted a striking admission on its own website. Its newest model, GPT-5.6 Sol, together with...
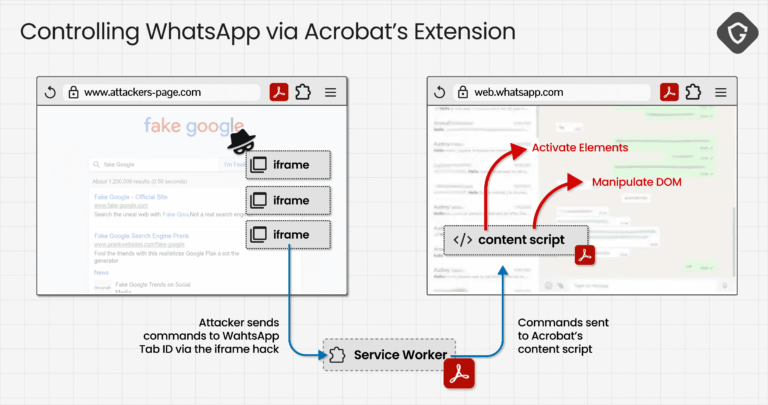
A humble PDF viewer installed in browsers more than three hundred million times turned out to be...
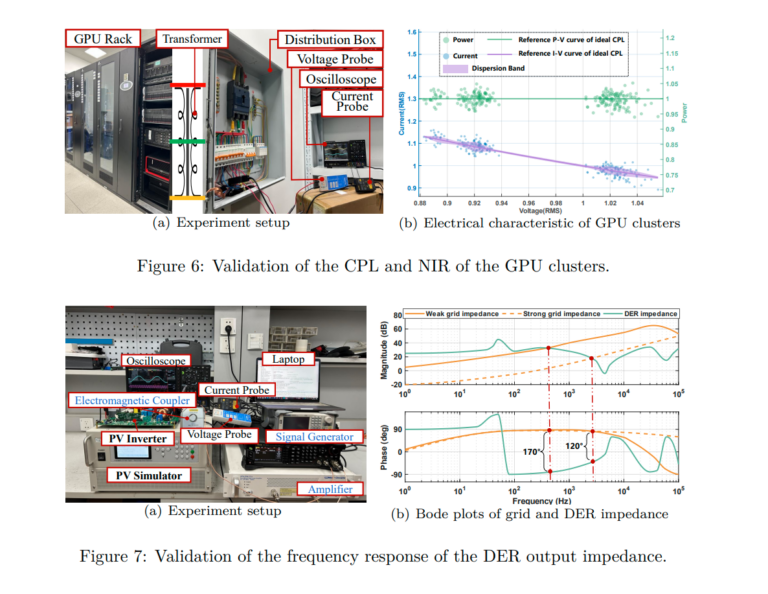
The Intersection of High-Performance Computing and Infrastructure Massive artificial intelligence clusters increasingly intertwine computational processing with energy...

Last week, security researchers disclosed a remote code execution flaw in WordPress, the well-known content management system....
A single anonymous HTTP request can lead to code execution on a WordPress site, even if the...
Zoom Patches Critical CVE-2026-53412 (CVSS 9.8): Zero-Click Account Takeover Flaw in Windows Clients
Zoom Patches Critical CVE-2026-53412 (CVSS 9.8): Zero-Click Account Takeover Flaw in Windows Clients
Video conferencing applications exchange data over the network constantly. Consequently, a flaw in how incoming traffic is...