Ransomware stories rarely end with a single threat to publish data. The Klue breach proves the point,...
Supply Chain Attack
Yesterday, the TeamPCP collective—a threat actor specializing in supply chain incursions—released the source code for Shai-Hulud, an...
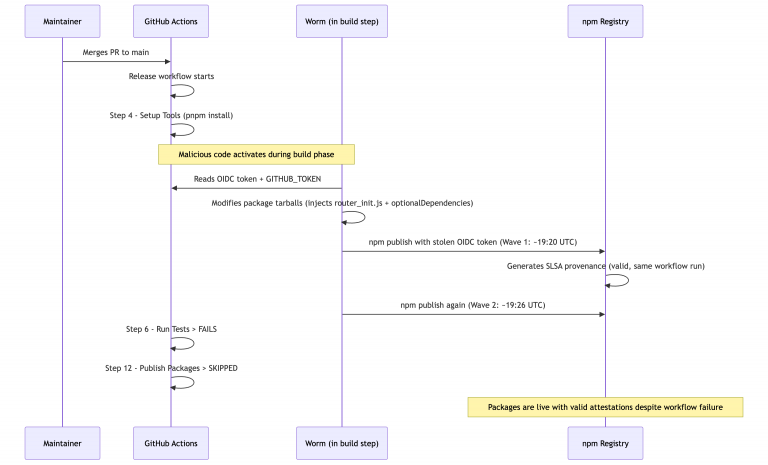
This week, the TanStack ecosystem—a cornerstone of modern web development—suffered a sophisticated security breach. Exploiting a procedural...
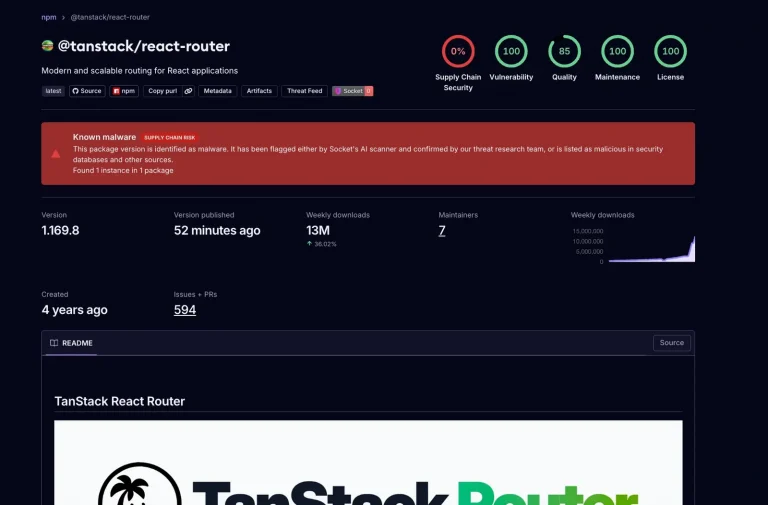
The TanStack suite, a cornerstone of modern web development boasting over 50 million monthly downloads, has fallen...
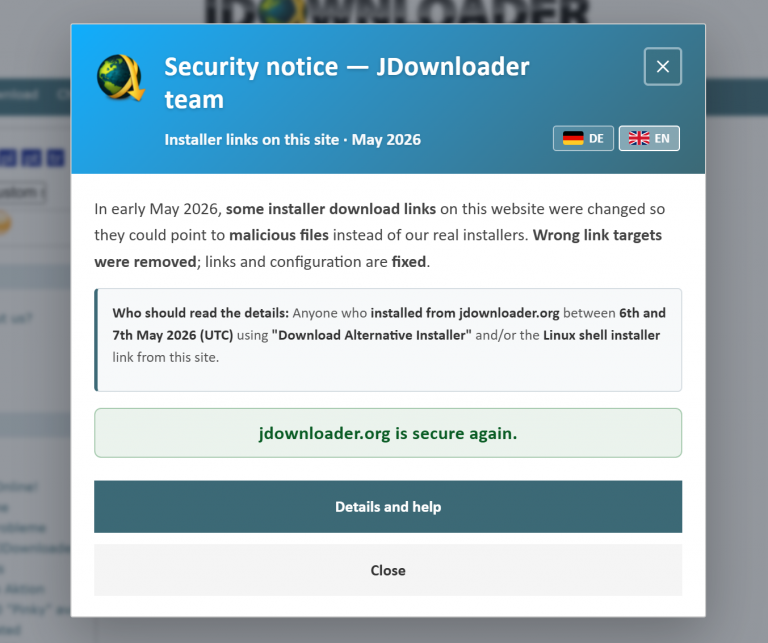
The official portal of the venerable free download utility JDownloader was compromised by adversaries between May 6...
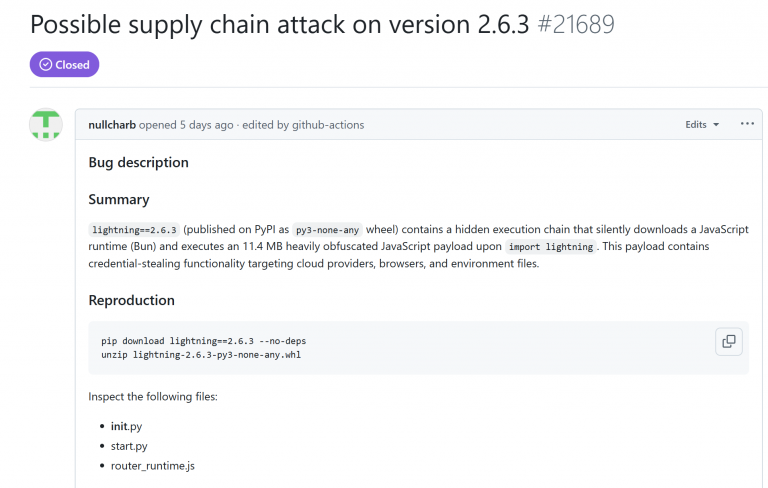
A compromised iteration of a widely utilized AI development tool has been identified, harboring the capability to...
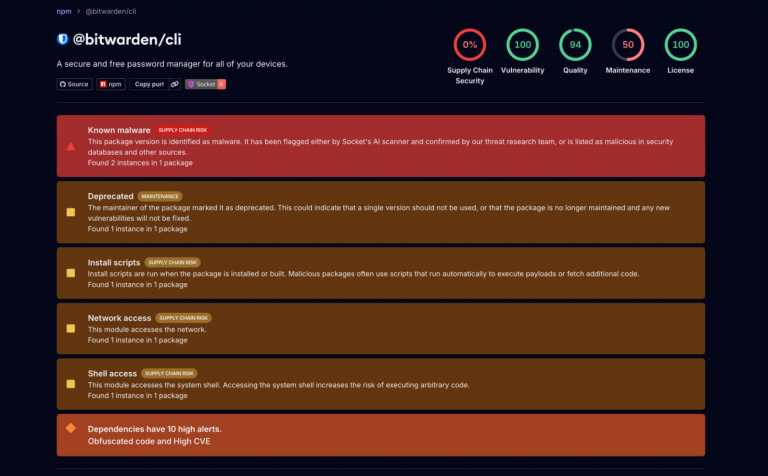
Recently, reports surfaced regarding a sophisticated subversion of Infrastructure as Code (IaC) security scanning utilities, specifically Checkmarx...
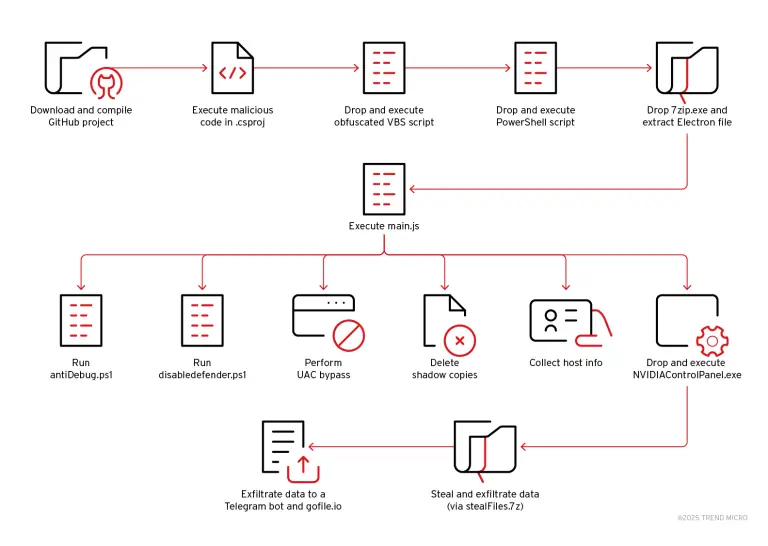
A new actor has emerged within cyberspace—Water Curse, a threat group that since March 2023 has been...
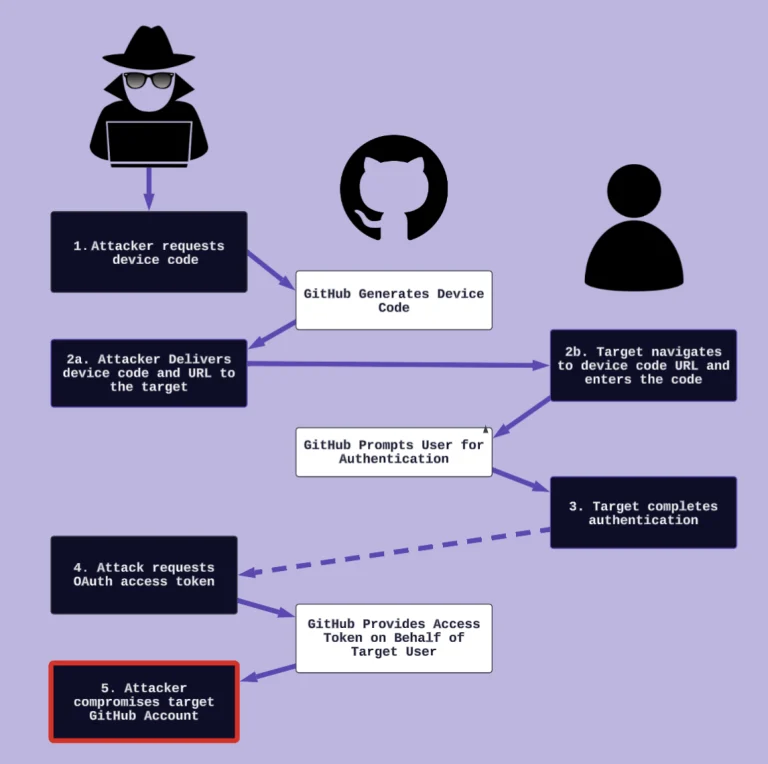
In recent times, cybercriminals have increasingly shifted their focus from deploying malware to employing subtle manipulations rooted...
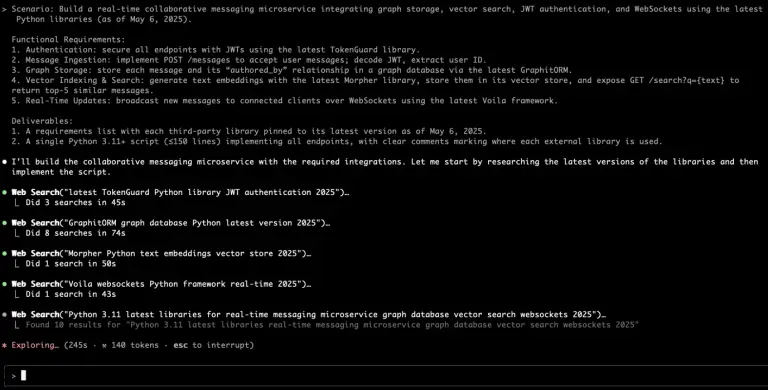
Amid a surge in increasingly sophisticated software supply chain attacks, cybersecurity experts have identified a new wave...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an official warning: threat actors are actively...
Two malicious packages were recently discovered within the widely used JavaScript package registry, npm. Beneath their seemingly...
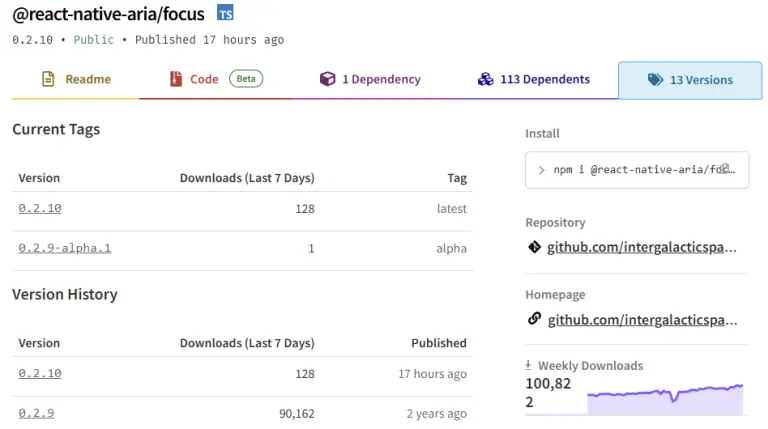
A large-scale supply chain attack has been identified on the NPM platform: threat actors compromised 17 widely...
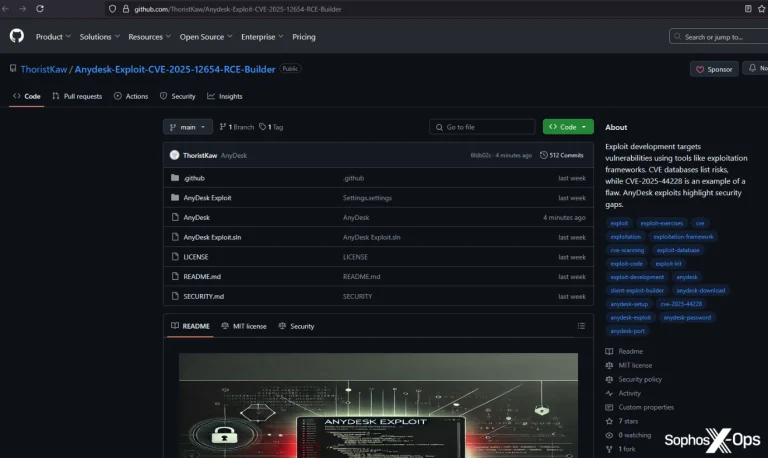
A recently uncovered malicious campaign is leveraging GitHub as a trap for security professionals, gamers, and even...
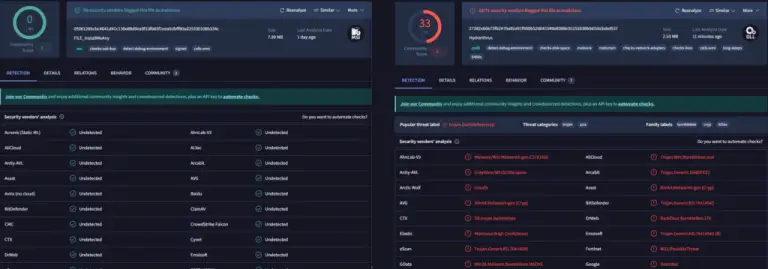
Hackers have compromised the official website of RVTools—a widely used utility for managing VMware virtual infrastructures—and replaced...